
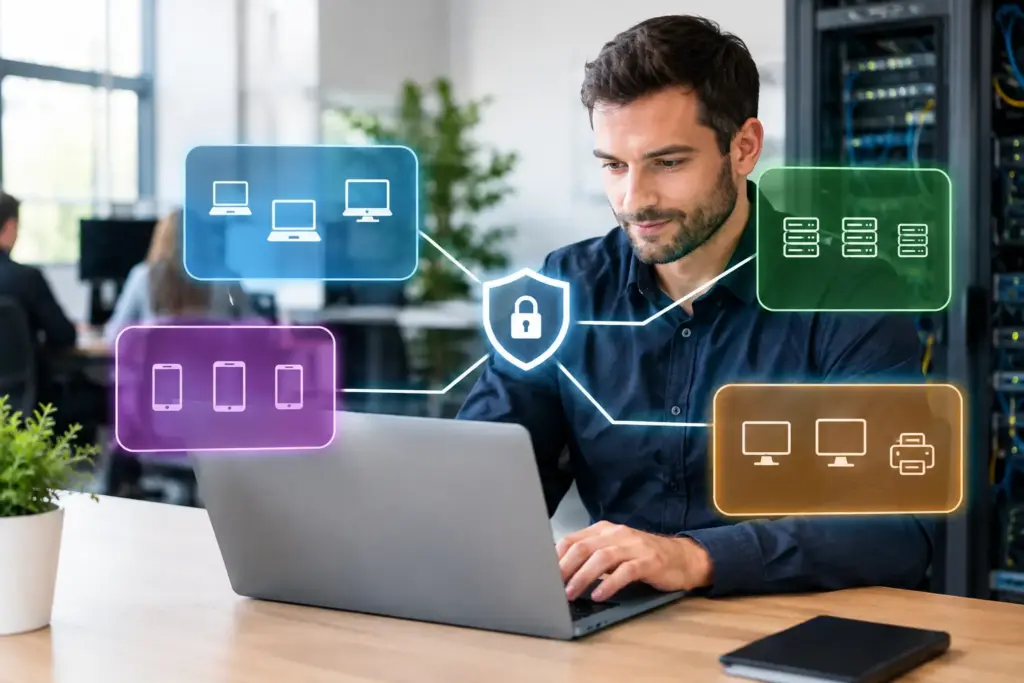
Anyone looking for network segmentation for an SME guideoften already has a recognizable problem: employees, printers, Wi-Fi, cloud applications, and sometimes even cameras all use the same network. That works fine, until a device causes a malfunction, an unauthorized visitor gains access, or ransomware spreads at lightning speed. Then it turns out that one large network seemed convenient, above all.
Network segmentation brings order. You divide your corporate network into smaller, protected sections. As a result, every device and every group of users only has access to what is needed. The result is not only better security, but also more clarity and less impact if something goes wrong.
Why a single network for everything is a risk
In many smaller organizations, the IT environment grows gradually. First, there are a few workstations and a printer. Then, wireless working, Microsoft 365, VoIP telephony, a meeting room, smart devices, and guest Wi-Fi are added. If everything remains on the same network, these components can unnecessarily interfere with each other.
Suppose a guest connects to your Wi-Fi. Without separation, that person could potentially see devices on the internal network. Or take an outdated printer: if it is misused, an attacker could use that single device to search further for files, workstations, or management systems. Not every incident immediately leads to data breaches, but you do want to keep the risk and the damage as low as possible.
You also notice the difference with ordinary outages. A camera that suddenly sends a lot of traffic or a defective device that burdens the network does not necessarily have an immediate impact on telephony and workstations. Segmentation limits the scope of such problems.
Network segmentation for SMEs: what do you separate?
Segmentation does not mean that you have to build a separate network for every device. That would be unnecessarily complicated and expensive. It involves logical groups with a similar function and the same level of security.
For most SMEs, structuring into four to six segments is a good starting point. Consider an internal network for workstations and managed mobile devices, a separate segment for servers or important business applications, a network for printers and other peripherals, and a completely separate guest network. If you use IP cameras, door access, conference screens, or other smart equipment, these usually belong in their own segment.
Separation is often achieved using VLANs, settings on managed switches, and firewall rules. You do not need to master these technical terms yourself to make the right choices. The core question is simpler: which device needs to be able to communicate with which system, and which connection is not needed at all?
A printer, for example, must be accessible from workstations but does not need unrestricted access to servers. Guests need internet access but not access to internal files or devices. A VoIP phone must be able to reliably call the telephony service but does not need access to your records.
Not everything needs to be nailed down
A common mistake is treating segmentation as an all-or-nothing project. A very strict setup can actually become a hindrance if processes grind to a halt as a result. A warehouse scanner that no longer communicates with the inventory package or a meeting room that no longer accepts a wireless presentation leads to frustration.
That is why you start with the most important divisions and build from there. The rules between segments must align with how your company operates. Security is only truly valuable if employees can work with it normally.
Start with an inventory that is accurate
Before adjusting settings, you need to know what is on the network. That sounds obvious, but many companies do not have an up-to-date overview. It then turns out that old access points, private devices, forgotten printers, or systems from external suppliers are connected.
Create a list of all devices and note for each device who owns it, what it is used for, and which connections are required. Do not look only at wired devices. Wi-Fi, remote working equipment, cloud management, and devices in meeting rooms are also part of the whole.
Next, ask practical questions. Do employees in the office need access to all systems? Do external technicians need temporary access? Which equipment is business-critical? And what is allowed to happen if a device is compromised? The answers help set priorities.
For an office with twenty employees, the initial setup can already be straightforward: workstations, telephony, printers, guests, and administration. A manufacturing company or healthcare organization often has additional requirements, for example regarding machinery, measuring equipment, or remote suppliers. The right design therefore depends on your working methods, not on a standard template.
Establish access rules before you set them
Segments in themselves offer no protection. The gain lies in the rules between those segments. Therefore, determine in advance which traffic you allow and what you block. The basic principle is simple: grant access only that is demonstrably necessary.
In practice, this means, for example, that workstations are allowed to print, but the printer segment may not independently establish connections to workstations. Guest Wi-Fi is granted access only to the internet. Management devices may access management systems, while regular users remain off-limits.
Document these choices in clear language. Note not only that a rule exists, but also why that rule is necessary and who is responsible. This prevents ambiguity when you later add a new application, an additional branch, or a different internet connection.
Also consider Wi-Fi and working from home
Separate guest Wi-Fi is a logical step, but corporate Wi-Fi deserves just as much attention. Employees should automatically be directed to the correct segment after logging in. Visitors receive a separate connection with their own password or login portal, without visibility into internal systems.
Remote workers usually connect directly to cloud applications such as Microsoft 365. However, remote access to files, servers, or management portals may still be necessary. In such cases, take a critical look at identity security, multi-factor authentication, and who has access. Office segmentation does not replace these measures, but together with good workplace management, it forms a much stronger foundation.
Choose management that suits your organization
With standalone consumer equipment, segmentation is often limited or difficult to manage. While you can create networks, the overview is lost as soon as there are multiple access points, switches, and locations. For a business environment, managed network equipment and central management are therefore usually more sensible.
This allows you to see which devices are connected, perform changes in a controlled manner, and identify anomalies more quickly. This is especially convenient when you do not have your own IT department. You prevent settings from depending on a single old password or on knowledge held solely by a former employee.
This does not mean you need the largest package right away. For a small office, a good firewall, managed switch, and business Wi-Fi may already be sufficient. With growth, multiple locations, or higher security requirements, the setup can be expanded further. Choose equipment and management that leave room for that next step.
Cloudformatie can assist with this through an inventory, a logical network design, and its management. This ensures that the setup remains tidy not only upon delivery but is also adapted as your business changes.
Testing and maintenance prevents a false sense of security
After setup, testing is necessary. Use real user scenarios to verify that employees can print, make calls, and work in the required applications. Also test what is specifically not allowed: can a guest device access internal systems? Can a printer unexpectedly access workstations? Does a telephone still function properly during peak load?
Subsequently, schedule regular times to assess the network. New equipment, renovations, a different internet connection, or a new cloud package may affect existing rules. Firmware updates and the removal of unused accounts and devices are also part of normal maintenance.
Pay attention to exceptions. In practice, a temporary rule for a supplier often remains in effect longer than intended. Keep track of such exceptions, assign them an end date, and regularly assess whether they are still necessary. It is precisely small loopholes that make a carefully managed network unmanageable again over time.
A feasible first step
You don't have to wait until your network needs to be completely rebuilt. Start by separating guest Wi-Fi and internal systems, map out your equipment, and determine which devices really need access to each other. Then, you can group printers, telephony, smart devices, and management systems into appropriate segments step by step.
A well-structured network is barely noticeable on most working days. Employees can continue working, guests can go online safely, and an outage is limited as much as possible to one part of the environment. This is precisely what makes network segmentation a practical choice for an SME that wants to grow without losing control of IT.